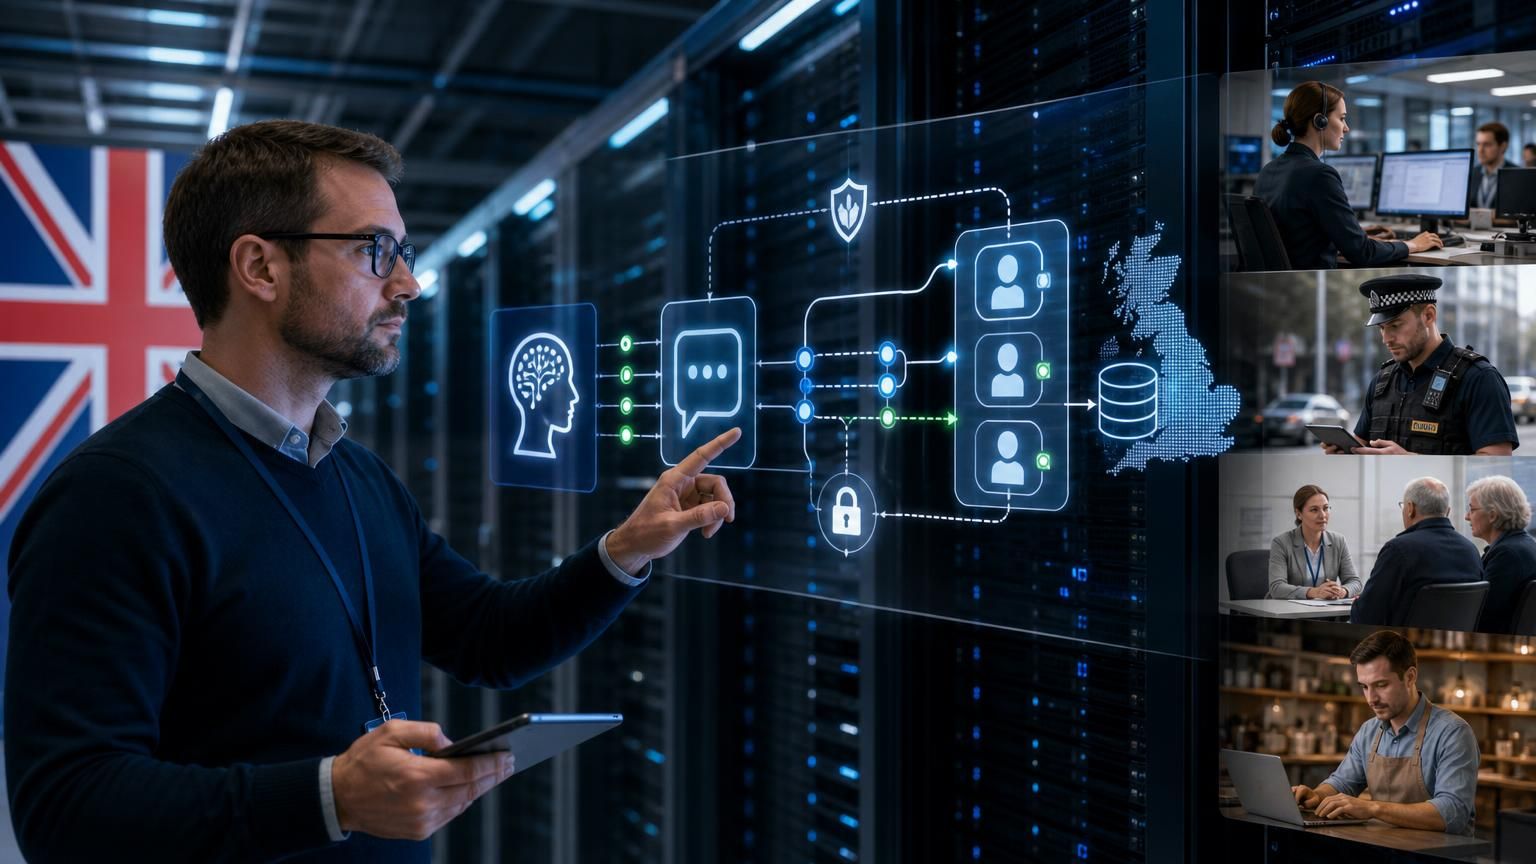
Why architecture matters for UK public and regulated services
Technical architecture decides whether a live chat deployment is a compliance risk or a revenue-driving support channel. For councils, police forces, housing associations and regulated businesses the priorities are clear: UK hosting and data residency, auditable handoffs, predictable fallbacks and integrations that don't leak sensitive data outside approved boundaries.
95% of UK IT leaders now list data sovereignty and residency as top concerns when deploying cloud services—so your architecture must make locality and control non-negotiable. ()
Clear definitions: rule-based bots, pure LLM bots and hybrid AI live chat
- Rule-based chatbots: deterministic flows, decision trees and hard-coded intents. Predictable, cheap, good for form-filling and transactional FAQs. They fail when user language drifts.
- Pure LLM bots: large language models generate free-form replies from prompts and broad training data. Strong at natural language but risky for regulated data, hallucinations, and non-deterministic outputs.
- Hybrid AI live chat: an engineered combination where LLMs or retrieval systems perform triage, knowledge lookup, and suggested responses, but a deterministic layer and human handoff ensure safety, auditability and SLA guarantees. Hybrid is the only practical model for high‑trust, UK-hosted public services.
Core architectural patterns for reliable hybrid live chat
Design patterns reduce surprises. Use these building blocks:
- Local-first data plane: host conversation logs, PII and sensitive context in UK data centers to satisfy procurement and audit needs. Tie storage to UK-controlled key management and retention policies.
- Triage + policy layer: let an AI layer classify intent and risk, but gate actions through a policy engine that enforces what the bot can and cannot do (e.g., no benefits advice beyond scripted answers without human approval).
- Context capture and summary: store the raw transcript, plus an indexed, time-stamped summary and the bot’s attempted steps. That makes handoffs fast and audit trails compact.
- Deterministic fallback engine: when confidence is below threshold, the system should follow a deterministic path—escalate, collect minimal extra verification data, or present a human-queue ETA.
- Seamless agent UX: handoffs must pre-populate an agent panel with the transcript, risk flags, AI-suggested answers and the escalation reason so the agent doesn’t ask the user to repeat themselves. Best-practice deployments reduce agent read-in time to under 30 seconds. ()
Rules for AI-to-human handoff (technical and UX)
Implement handoff triggers both explicit and implicit:
- Explicit triggers: user taps “speak to agent” or selects escalation intent.
- Confidence-based triggers: model confidence below a configurable threshold.
- Pattern triggers: repeated rephrasing, long latency, or sensitive topics (safeguarding, legal, benefits, crime reports).
- Time-based triggers: if a bot exchange exceeds X turns, automatically triage to human.
When handoff occurs, transfer:
- Full raw transcript.
- Structured metadata (intent, confidence, risk tags).
- AI attempted actions and why they failed.
- Source documents used by the AI (if RAG was used).
These principles align with practical handoff playbooks used across 2024–2025 deployments. ()
Fallback logic: make failure predictable and auditable
Fallbacks should be a feature, not an afterthought:
- Conservative defaults: when uncertain, escalate or restrict rather than guess.
- Audit tags: every fallback must be tagged with a reason code and retention policy.
- User-facing clarity: tell the user why the bot stopped and what happens next (e.g., ETA, documents required).
- Escalation routing: map reason codes to specialist queues—safeguarding, licensing, housing repairs—so the right team gets the case first time.
Hybrid deployments that adopt deterministic fallbacks reduce inappropriate automated replies and limit regulatory exposure.
Integrations and composability: keep control of data flows
Integrations are where policies break. Design a strict integration model:
- Outbound via vetted connectors: use controlled adapters for CRM, case management and authentication systems.
- Local caching for sensitive lookups: pull only non-sensitive IDs across borders; resolve details in UK-hosted cache.
- AI tool integrations: when the hybrid stack calls external AI (for retrieval or LLM), route only redacted or tokenised queries and maintain a UK-hosted index or RAG store. IMSupporting documents on AI tool integration explain practical adapter patterns and safeguards. Hybrid AI chat workflows and AI tool integrations guidance are good implementation references.
The NCSC cloud security principles reinforce that you must understand whether provider jurisdictions affect your ability to meet legal obligations—this should shape your cloud and vendor selection. (ncsc.gov.uk)
Compliance: retention, transparency and public‑sector procurement
- UK hosting and keys: store transcripts and keys in the UK. That removes ambiguity in Freedom of Information, FOI and audit requests.
- Data minimisation: keep only fields required for the case life-cycle; redact downstream AI logs where possible.
- Audit-ready trails: build immutable timestamps and human-agent sign-offs for decisions that affect people (benefits, enforcement, safeguarding).
The UK is formalising expectations for public-sector AI use; practical policies and internal AI frameworks are already in circulation and should inform procurement and design. (ico.org.uk)
Operational reliability: monitoring, SLAs and runbooks
- Monitor end-to-end metrics: handoff latency, agent read-in time, transcript completeness, fallback rates, and false escalation rates.
- Set SLAs by intent severity: safeguarding escalations should have different SLA targets than general enquiries.
- Continuous testing: synthetic traffic that exercises edge cases, privacy leaks, and escalation paths is essential before any release.
Where implemented well, intelligent handoff systems increase customer satisfaction significantly—hybrid systems that get the handoff right report markedly better CSAT. ()
Practical implementation checklist (30–90 day roadmap)
- Day 0–7: Define data residency, encryption and retention policies.
- Week 2–4: Map intents and sensitive topics; design gate policies for each.
- Month 1–2: Build UK-hosted transcript store, agent panel and handoff payload format.
- Month 2–3: Integrate with CRM and case systems via vetted adapters; implement deterministic fallbacks.
- Month 3+: Run pilot with logged-only mode, iterate thresholds and publish runbooks and agent coaching flows.
Next step and recommended partner approach
If you’re a council, police team, housing association or regulated business, start with a UK-hosted hybrid proof-of-concept that isolates sensitive data and proves handoff workflows under real conditions. Read IMSupporting’s hybrid workflow and tool-integration pages to compare technical patterns: https://imsupporting.com/feature-hybrid-ai-chat-workflows.php and https://imsupporting.com/feature-ai-tool-integrations.php.
For an immediate architecture review and a pilot scoped around UK hosting, fallback rules and audit trails, contact IMSupporting and request a tailored runbook and deployment plan: https://imsupporting.com/.
Takeaway: hybrid AI live chat is not about swapping humans for models—it's about engineering a safe, auditable, UK-hosted pipeline that uses AI for triage and knowledge while giving humans clean, context-rich handoffs. That combination keeps citizens safe, IT teams confident and senior leaders on the right side of procurement and compliance.